



Glossary of Compliance
Compliance Glossary
Our list of curated compliance glossary offers everything you to know about compliance in one place.
In-house Recovery
In-house recovery means recovery of a dedicated physical server or an in-house server amid data replication or when there is a disaster.
Additional reading
What Is PHI in HIPAA: 18 Identifiers With Examples (2026)
TL;DR PHI stands for Protected Health Information – in HIPAA, it refers to any health, treatment, or payment data that can be used to identify an individual, whether in written, oral, or electronic form. PHI includes 18 identifiers such as names, addresses, phone numbers, Social Security numbers, email addresses, and full-face photos. Protected Health Information…
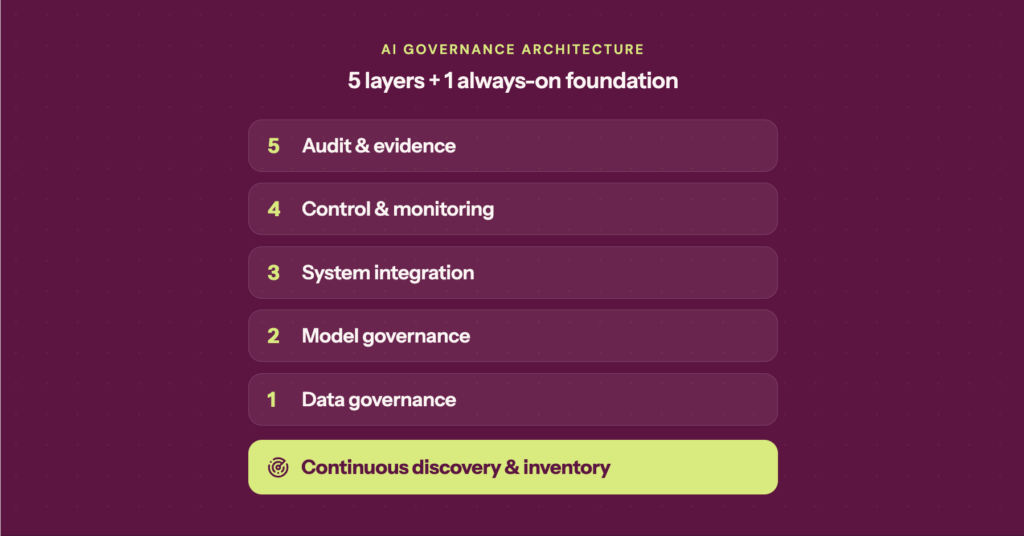
How to Build an AI Governance Stack That Runs Continuously
TL;DR Most organizations already have, or are building, AI Governance in some form. Precisely 69.9% as per Sprinto’s CISO Pulse Check Report released earlier this year. Moreover, only 52.81% of GRC teams even track AI as a separate category, let alone ensure AI risk is being governed continuously. But what happens to AI Governance when…
Guide to Building a High-Leverage TPRM Program (Without Drowning in Spreadsheets)
As you grow beyond early-stage SaaS, enterprise buyers stop accepting trust-me slides. They want proof that the vendors, processors, sub-processors, and partners in your ecosystem are secure, resilient, and reviewed on a repeatable cadence. That is where a third-party risk management (TPRM) program helps. The goal is not to send a 200-question assessment to every…

Sprinto: Your growth superpower
Use Sprinto to centralize security compliance management – so nothing
gets in the way of your moving up and winning big.



