



Glossary of Compliance
Compliance Glossary
Our list of curated compliance glossary offers everything you to know about compliance in one place.
Critical Infrastructure
Critical infrastructure describes the physical assets and I.T. systems that are so vital to the enterprise that their destruction or incapacity would have a devitalizing impact on the economic or physical security or public health and safety.
Additional reading

Top 6 Drata Alternatives & Competitors in 2026
TL; DR Drata helps organizations become audit-ready quickly, but challenges may arise after onboarding. Customers often find that add-ons increase the total cost, evidence uploads cannot be edited, and teams may need to re-upload documents when changes occur. This guide compares six Drata alternatives, highlighting their advantages in automation, evidence management, reporting, and scalability to…

PCI Vulnerability Scan: A Complete Compliance Guide
TL,DR: A PCI vulnerability scan is an automated test identifying potential network vulnerabilities. PCI DSS requires all organizations to conduct both internal and external scans at least quarterly and after substantial network changes External scans must be performed by a PCI SSC Approved Scanning Vendor (ASV) covering public-facing systems. Internal scans focus on hosts, servers,…
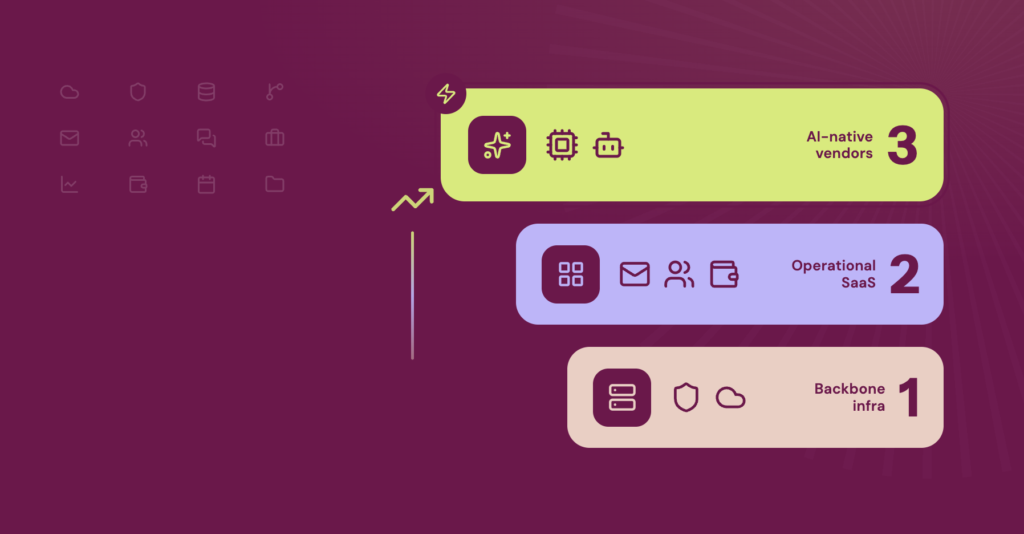
The New Vendor Tiering Model: How to Categorize Vendor Risk in an AI Era
TL;DR AI is changing vendor tiering because risk is no longer limited to core infrastructure vendors. Traditional backbone categories like cloud, cybersecurity, and DevOps still require the highest governance rigor, but AI integrations are now expanding runtime exposure across CRMs, collaboration tools, HR systems, finance platforms, and other operational SaaS categories. At the same time,…

Sprinto: Your growth superpower
Use Sprinto to centralize security compliance management – so nothing
gets in the way of your moving up and winning big.



