



Glossary of Compliance
Compliance Glossary
Our list of curated compliance glossary offers everything you to know about compliance in one place.
Registration
During the 2 to 3 months your company is still building its quality system, you’ll need to begin searching for an ISO registrar on the ANSI-ASQ National Accreditation Board (ANAB) to select the registrar right for you. Registrars must fulfill the requirements of the ISO Accreditation Bodies.
Additional reading

Article 28 of GDPR: The Essentials for Data Processors
TL,DR: GDPR Article 28 establishes the Data Processing Agreement (DPA) between controllers and processors, defining the legally binding boundaries and obligations for all personal data handling activities Controllers must only work with processors producing evidence of sufficient technical and organizational safeguards under Article 32. Processors must follow all written instructions and obtain prior authorization before…

PCI DSS Compliance: Complete Guide
TL,DR: PCI DSS compliance protects cardholder data through 12 requirements and 250+ security controls. Merchants and service providers must validate compliance annually and maintain controls year-round. The guide covers PCI levels, SAQs, risk assessments, gap remediation, control monitoring, and involved parties. As a founder of a business that processes online transactions, PCI compliance is mandatory,…
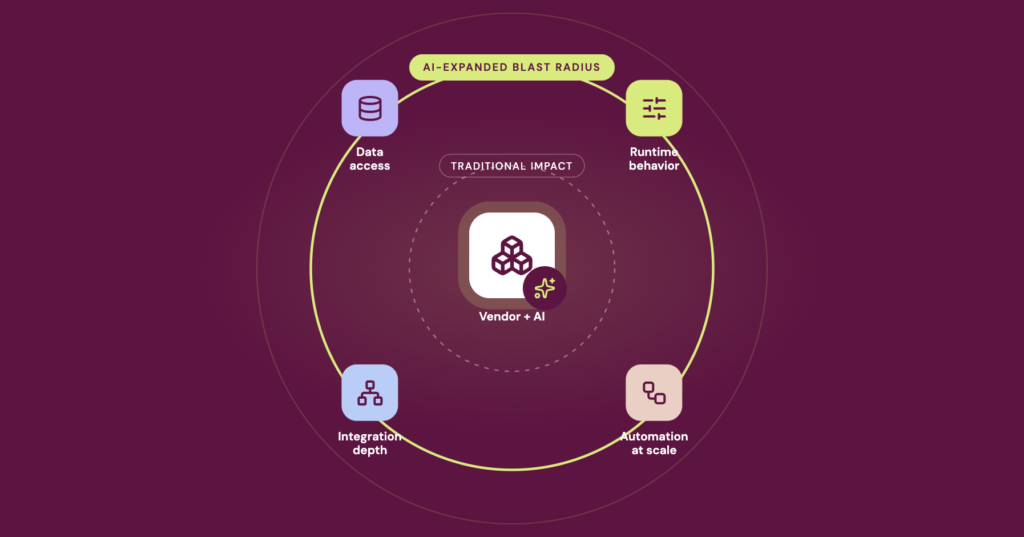
201-Vendor Study Uncovers How AI is Driving Risk and Blast Radius
TL;DR AI is being embedded into vendor products faster than third-party risk management programs can assess it. CRMs, HR platforms, customer support tools, and dozens of operational SaaS categories now route data through AI inference layers that didn’t exist when those vendors were originally onboarded. Sprinto’s Vendor Category Landscape 2026 maps where this exposure is…

Sprinto: Your growth superpower
Use Sprinto to centralize security compliance management – so nothing
gets in the way of your moving up and winning big.



