



Glossary of Compliance
Compliance Glossary
Our list of curated compliance glossary offers everything you to know about compliance in one place.
Direct Treatment Relationships
A healthcare provider is said to have a Direct Treatment Relationship with the patient if they provides services, diagnoses, products, or results directly to the patient.
Additional reading
Service Organization Controls (SOC) Reports: Types & Step to follow
In late 2023, the AICPA refreshed its Trust Services Criteria on September 30 and followed up on October 1 with a detailed attestation guide for SOC for Cybersecurity engagements. That summer, the SEC’s July 26 rule began requiring public companies to disclose material cybersecurity incidents within four business days and outline their risk-management governance in…

Drata Vs Secureframe: Compare All Differences 2026
TL;DR While both, Drata and Secureframe are capable GRC automation tools, the nuanced differences in pricing, AI and automation capabilities, and support can make all the difference for your team. In this blog, we dive deep into the capabilities of the platforms and compare them against 10 key areas to conclude which platform is better…
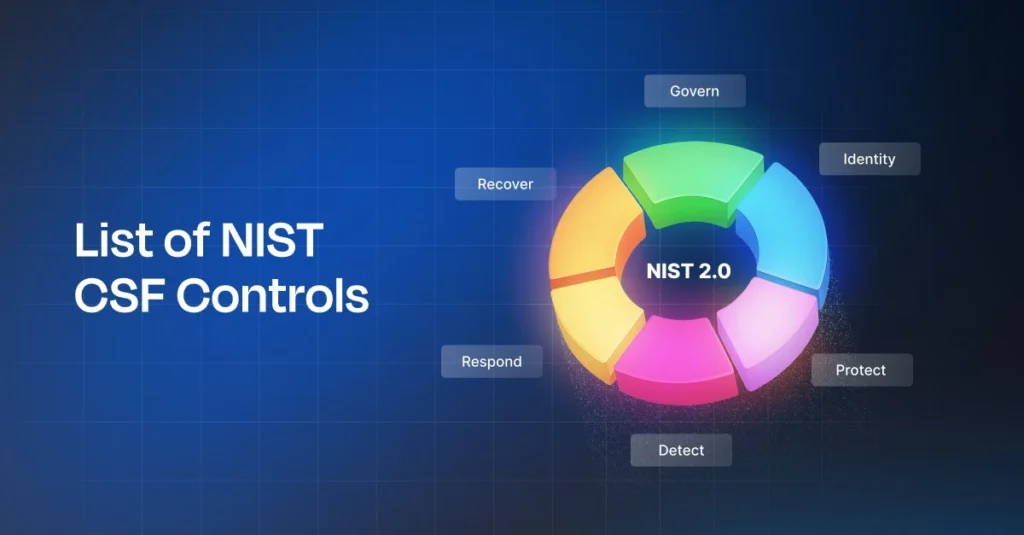
List of NIST Cybersecurity Framework Controls
TL;DR The NIST CSF, developed by the National Institute of Standards and Technology (NIST), whose mission is to enable U.S. innovation and competitiveness in industry, provides a voluntary yet systematic framework for cybersecurity risk management. Effective deployment of the NIST CSF entails tailored application of its core functions, maturity tiers, and profile tailored to the…

Sprinto: Your growth superpower
Use Sprinto to centralize security compliance management – so nothing
gets in the way of your moving up and winning big.



