Glossary of Compliance
Compliance Glossary
Our list of curated compliance glossary offers everything you to know about compliance in one place.
ISMS
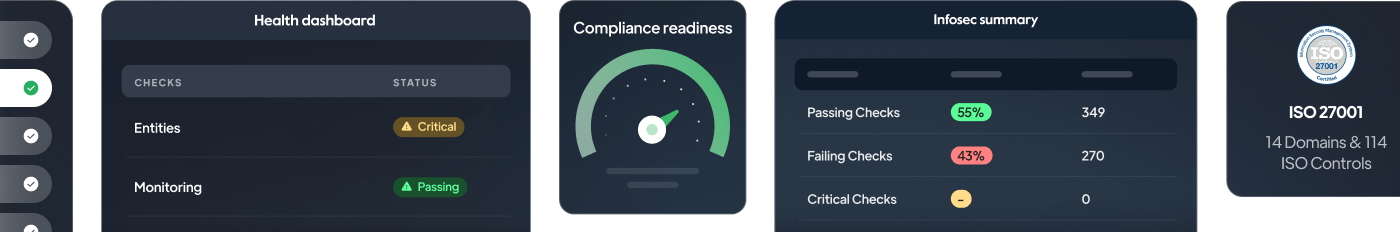
ISMS or information security management system (ISMS) is a set of procedures and policies for systematically managing an enterprise’s sensitive information. The goal of an ISMS is to detect and minimize the risk while ensuring business continuity by proactively countering the impact of a security breach.
Additional reading
Understanding Different Types of Compliance Audits
TL;DR Compliance audits help you prove that your controls, policies, processes, and evidence meet the requirements your business is accountable for. These requirements may come from regulations, industry standards, customer contracts, internal policies, or certification frameworks. This guide breaks down the main types of compliance audits by who performs them and by what they test….
Compliance Best Practices: How to Stay Ahead of Regulatory Challenges
Running compliance projects is pretty much like a circus. You are juggling multiple things at once—all goes fine until an important bit fails, and chaos unfolds. Before you know it, your team is putting out fires, trying to put broken systems back together, and not knowing how to keep things in motion. While there is…
Choosing the Perfect Cybersecurity Vendor: A Step-by-Step Guide
TL,DR: A cybersecurity vendor delivers services and solutions to safeguard organizations against cyber threats. Selection starts with identifying critical data assets across 6 criteria from strategic importance to operational continuity dependency Key evaluation factors include the vendor’s compliance framework coverage, integration compatibility with existing infrastructure, incident response capabilities, threat intelligence resources, scalability for growth, and…

Sprinto: Your growth superpower
Use Sprinto to centralize security compliance management – so nothing
gets in the way of your moving up and winning big.