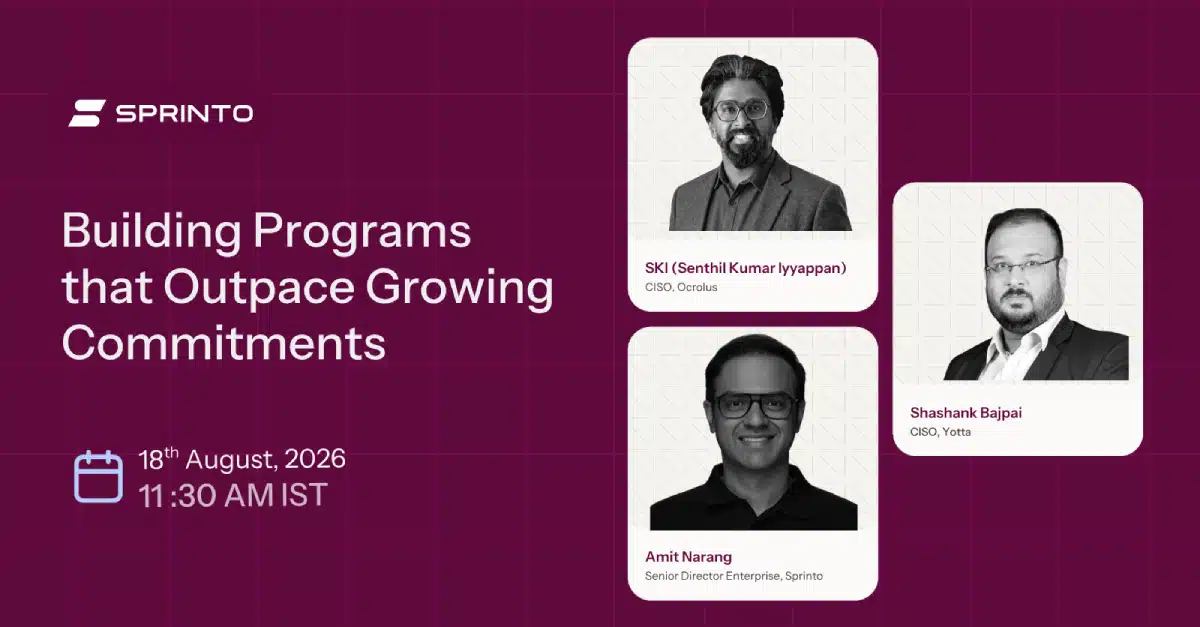
SKI (Senthil Kumar Iyyappan)Chief Information Security Officer & CTSO,Ocrolus
Amit NarangSenior Director Enterprise APAC & EMEA,Sprinto
Shashank BajpaiCISOYotta
Commitments pile up from regulations, customer contracts, vendor agreements, AI policies, and insurance. Each has a different owner and timeline, and rarely a shared place to track them. Most teams manage this through periodic audits and compliance sprints, which works until something breaks. Shashank Bajpai (CISO, Yotta) and Senthil Kumar Iyyappan (CISO & Head of IT, Oculus) share how they run programs that stay ahead of this sprawl.
You’ll walk away knowing
How to design a control framework that meets multiple frameworks and customer-specific requirements from one foundation.
How ownership should split across legal, engineering, and security, so it doesn’t all default to security.
Why delayed discovery is the real cost of a compliance gap, and what continuous monitoring looks like in practice.
Related event and webinars
WEBINAR
Turning SOC 2 Pressure Into Competitive Advantage
Watch Now
WEBINAR
Building Programs That Outpace Commitments
Watch Now
WEBINAR
Responding To Exceptions and Ensuring They Stay Resolved
Watch Now
Sprinto: Your ally for all things compliance, risk, governance